


What AI governance consulting includes
Aranv offers AI governance consulting for small and midsize businesses that use or build AI tools. We write practical usage policies, review each AI use case for risk, set data handling rules and put guardrails on AI agents, so leaders know what AI is doing in the business and why.
We start with an inventory: the AI tools staff already use, AI features switched on inside your SaaS products, and anything built in-house. Features enabled by default in software you already pay for are easy to miss. Each item gets an owner, a purpose and a note of the data it touches.
Reviews follow the structure of the NIST AI Risk Management Framework, which organizes the work into four functions: govern, map, measure and manage. For security testing we use the OWASP Top 10 for LLM Applications as a checklist, covering risks such as prompt injection, sensitive information disclosure and excessive agency.
The governance loop for each AI use
Inventory, assess, control, monitor
- 01 List every AI use Tools staff use, AI features inside your software and systems you have built.
- 02 Assess the risk Data involved, decisions affected, who could be harmed and which laws apply.
- 03 Set controls Approved tools, data rules, human approval points and limits on agent permissions.
- 04 Monitor and review Logs, spot checks and a scheduled review as tools and rules change.
Review depth follows the risk: a writing aid needs less scrutiny than a credit or hiring decision.
Common AI governance needs
Enterprise AI governance programs are heavy for a growing company. These are the pieces that matter at your size.
AI usage policy
A short policy on which AI tools staff may use, with which data, and what must be checked before output is used.
Use-case risk review
Each new AI project gets a brief assessment of data, impact, failure modes and controls before it is built.
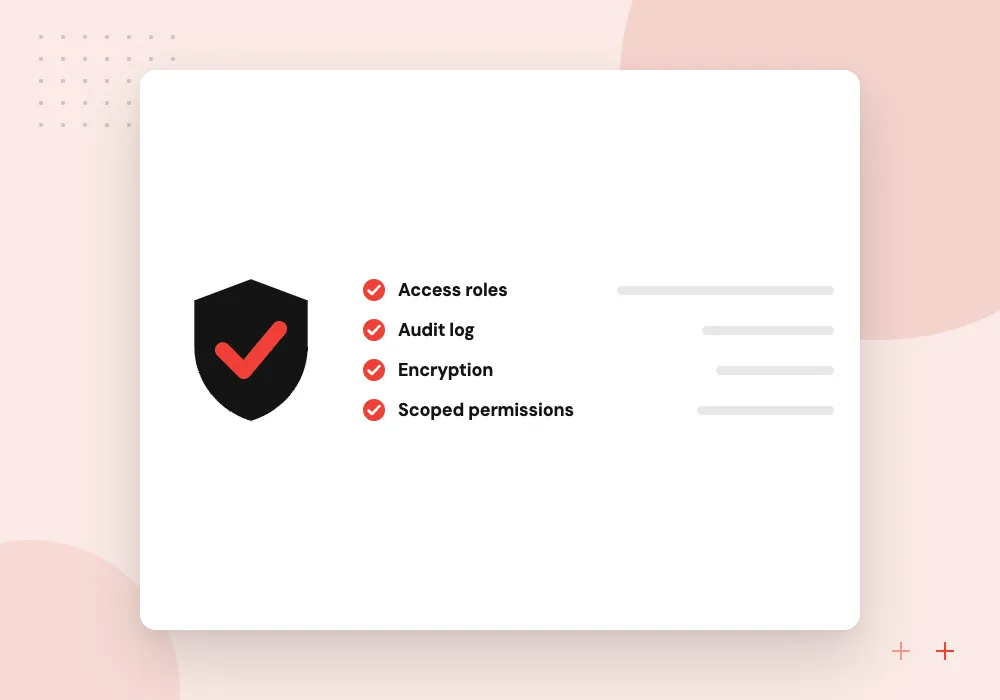
AI agent security
Agents get least-privilege access, approval gates for risky actions and defenses against instructions hidden in emails or files.
Vendor and model review
AI vendors are checked for data retention, training use, hosting region and contract terms before you sign.
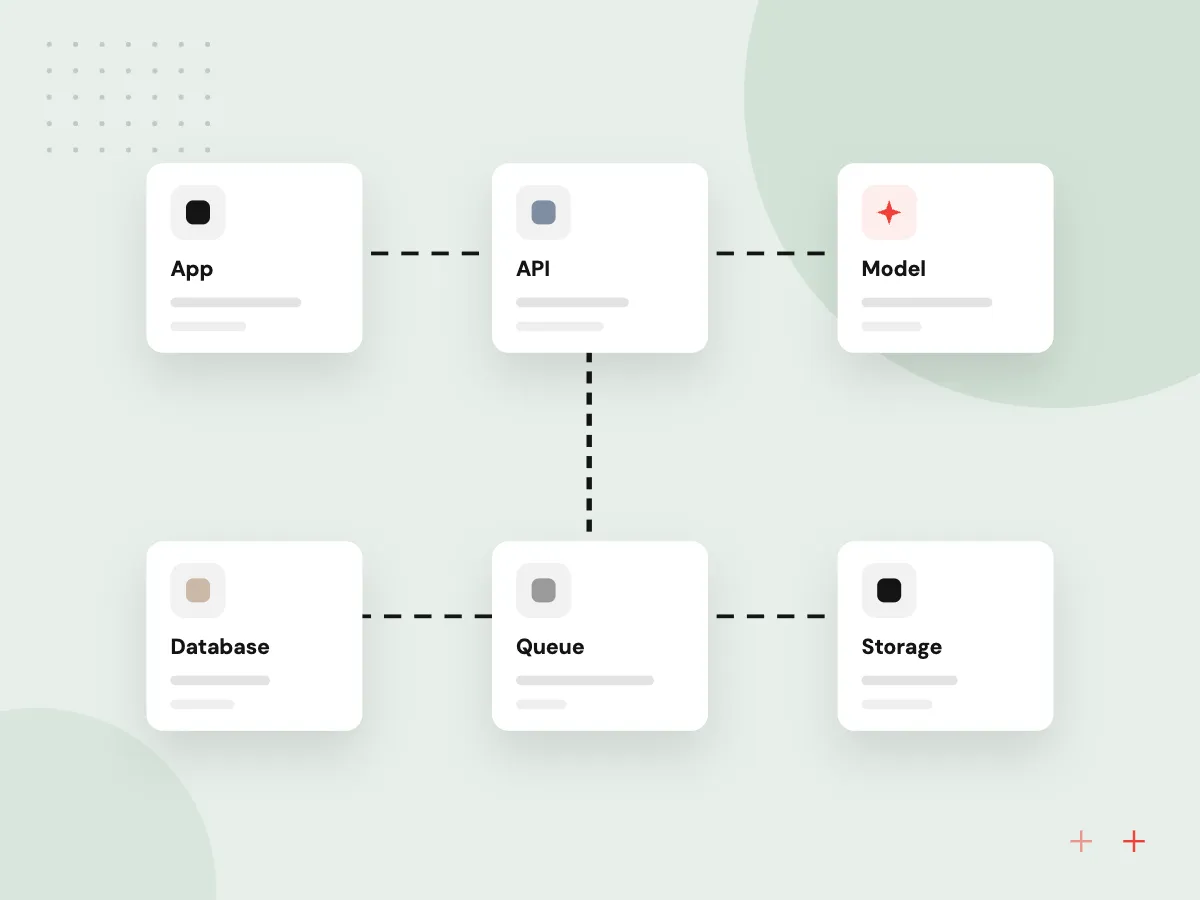
Data classes and where each may go
We sort your information into a few classes, such as public, internal, customer and regulated, and state which AI tools and providers each class may reach. The rules also cover retention and training settings, masking of personal details and who may switch on a new AI feature in your software.
What we do
- Data classes with plain examples
- Approved tools for each class
- Provider retention and training settings
- Masking rules for personal details
- Owner for enabling new AI features
Injection and permission tests for agents
Before an agent goes live we try to make it misbehave. Test emails and files carry hidden instructions, requests push it toward tools outside its role, and we confirm that approval gates hold, each tool call is logged and the agent stops when it reaches its limits.
What we do
- Hidden-instruction test documents
- Checks on tool and record scope
- Approval gate tests
- Tool call log review
- Written findings with fixes
How we approach a project
Agents need extra care because they act, not just answer. We limit each agent to the tools and records it needs, require approval for payments, deletions and external messages, and treat content from emails and documents as untrusted. These controls are built into projects from our agentic AI development and AI agent development teams.
Contracts and data handling are settled with your legal and IT leads, and our security, NDA and IP page explains how we treat your code and data. If you sell into the EU or a regulated sector, your counsel confirms which laws apply.
Governance belongs in planning, not after launch. Our AI consulting engagements and the AI project readiness checklist both include a risk step before any build begins.
How we work
- Proportionate to real risk
- Policies people can actually follow
- Evidence kept for every decision
Our Process
-

Discovery interviews
We talk with leadership, IT, legal and the heaviest AI users to learn goals, concerns and current practice.
-

Inventory and gap review
We list AI uses, rate each by risk and compare current controls with the framework and your obligations.
-

Policies and guardrails
We draft the usage policy, review templates and technical guardrails, then agree them with your leads.
-

Adoption and review cycle
Staff get a short briefing, owners get review templates, and a recurring review date goes in the calendar.
Why Aranv for AI governance
Builders, not only advisers
The people writing your controls also build AI agents and integrations, so each rule is something that can be configured, tested and logged in your real systems.
Sized for a growing company
Policies stay short enough for staff to read, and review forms take minutes to complete. Heavier process is added only where customer data, money or decisions about people are involved.
Clear about our limits
We do not certify, audit or give legal opinions. Your counsel decides which laws apply, and we turn that advice into settings, checks and records.
Evidence you can show later
Every review, approval and exception is recorded with a date and an owner, so a customer security questionnaire can be answered without rebuilding the history.
Planning AI Governance and Security Consulting?
Book a 30-minute conversation with the team that would build it.
AI governance FAQs
-
Does a small business need AI governance?
Yes, scaled to its size. If staff paste customer data into AI tools, or an AI system touches decisions about people, money or safety, you need written rules. For a small team that can be a two-page policy and a short review for each new use.
-
What is AI governance?
It is the set of policies, roles and controls that decide which AI is used, with what data, for which decisions, and how results are checked. Good governance makes AI use visible and accountable without blocking useful tools.
-
How do you secure AI agents?
Give each agent only the permissions its task needs, require human approval for high-impact actions, treat retrieved content as untrusted, log every tool call and test the agent against prompt injection before launch.
-
Can you certify us or make us compliant?
No. We do not issue certifications or legal opinions. We help you put practical controls in place and keep evidence of them, which supports your own compliance work and any audit you choose to pursue with an accredited body.
-
Which frameworks do you use?
The NIST AI Risk Management Framework and its Generative AI Profile shape our reviews, and the OWASP Top 10 for LLM Applications guides security testing. If you already follow ISO/IEC 42001 or another standard, we align with it.
-
How long does an AI governance review take?
It depends on how many AI uses you have and how many teams are involved. A focused review of policies and a handful of use cases is a short engagement, and follow-up reviews then run on a schedule you set.

Let’s talk about your next step
Contact Aranv to discuss your workflow, current tools, and goals. Meet with our team or send an inquiry.
Book a meeting with our team
Choose an available date and time for a 30-minute conversation about your project.
Tell us about your project
Share a few details so we can discuss a useful next step.
Prefer email? sales@aranv.com